
Risk Management
NSK’s Approach
NSK defines the purpose of enterprise risk management (ERM) as “effectively utilizing Group-wide resources and managing the impact of uncertainty related to the realization of the NSK Group Corporate Philosophy and the achievement of management goals.” ERM consists of two components: “risk management,” which aims to manage impacts due to uncertainty, and “incident management,” which aims to manage the response to incidents and accidents that have already occurred.
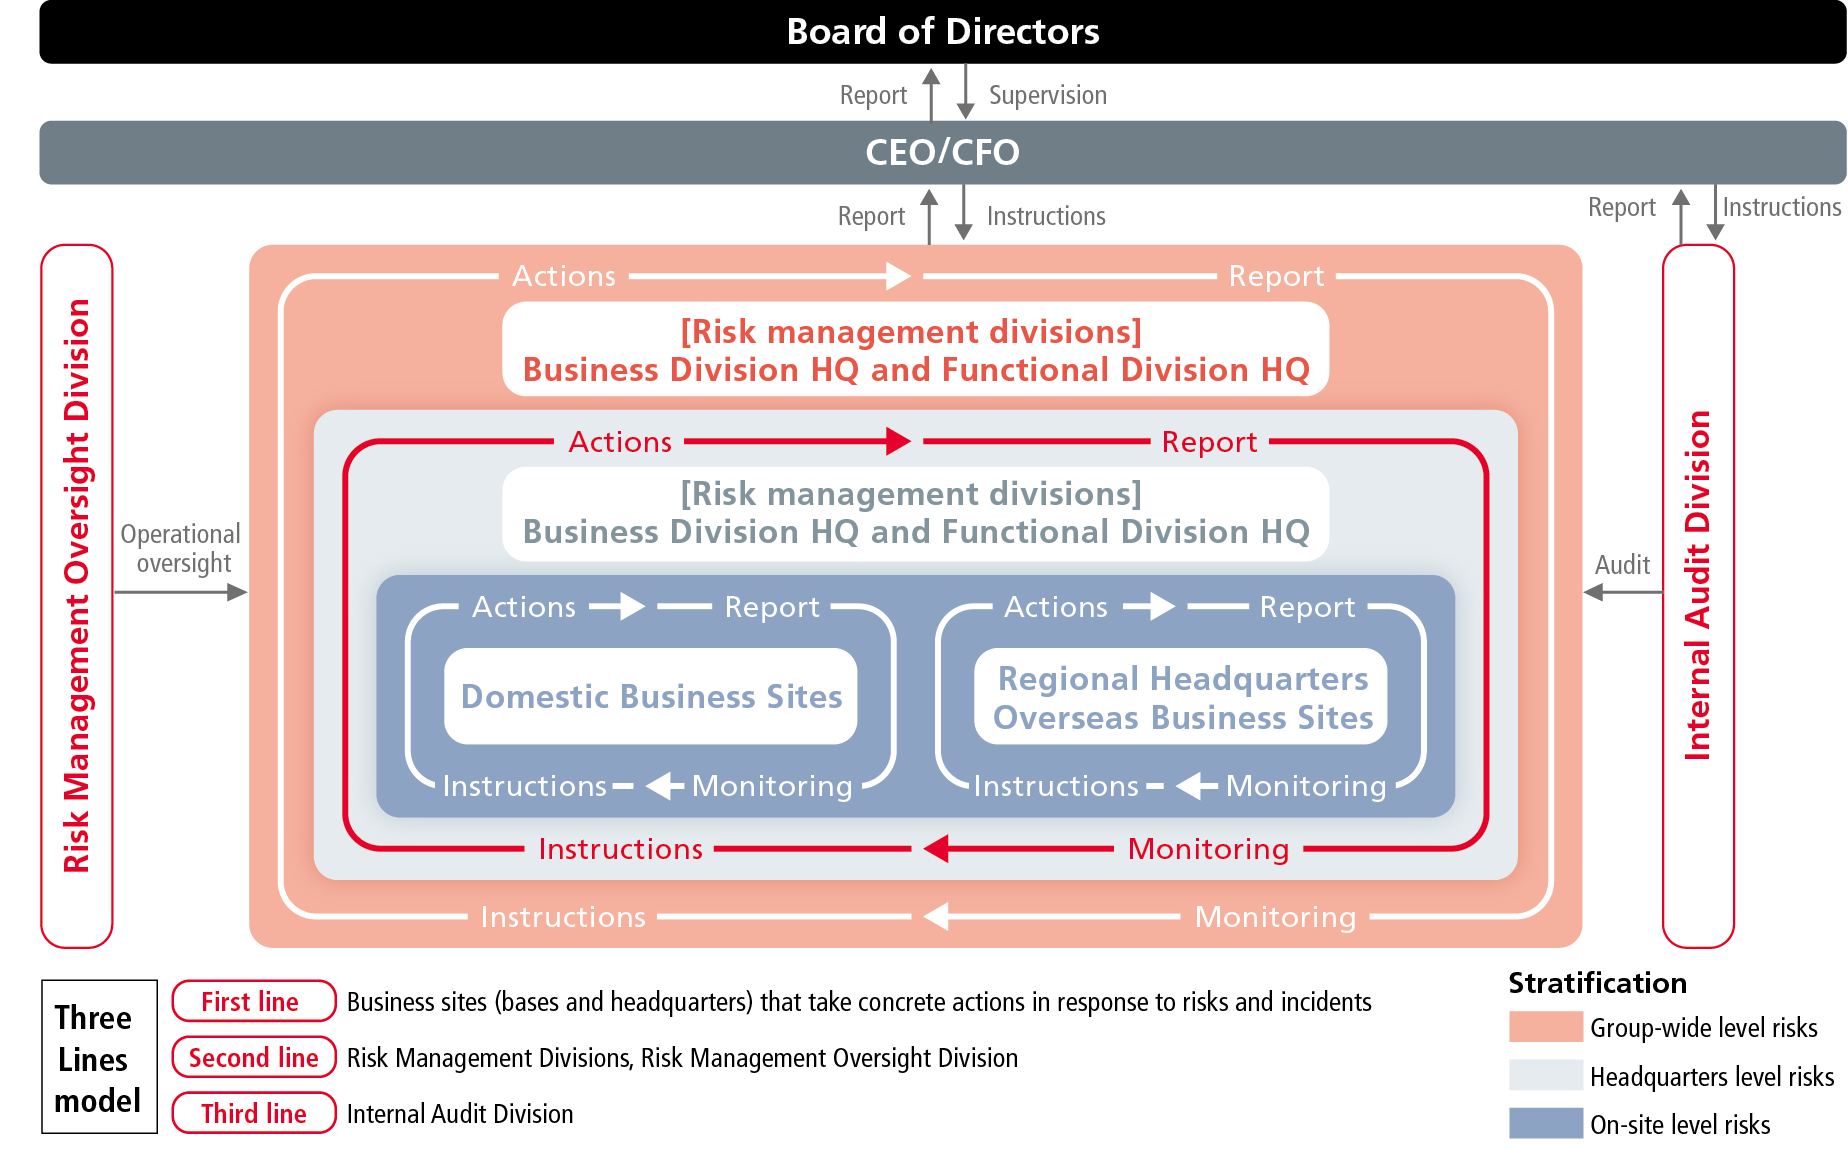
To achieve the purpose of ERM, based on the “Three Lines” model, NSK has established a management and governance framework that stretches from the Board of Directors to each site within the Group. Under this framework, risk management and incident management are conducted. The details are as follows.
ERM System
◆Management and Governance Framework
We have designated the companies, sites, and divisions that are actually exposed to risks or where incidents occur, such as plants and sales offices, as first-line risk response divisions. In addition, we have established second-line risk management divisions with responsibility for managing risks and incidents related to different types of risk. We have also created the Risk Management Oversight Division to oversee ERM as a whole and support the CEO and CFO in being able to supervise the status of risk and incident management by the risk response divisions and the risk management divisions. Finally, the Internal Audit Department serves as the third line, auditing the status of activities by the first- and second-line divisions and evaluating their effectiveness.
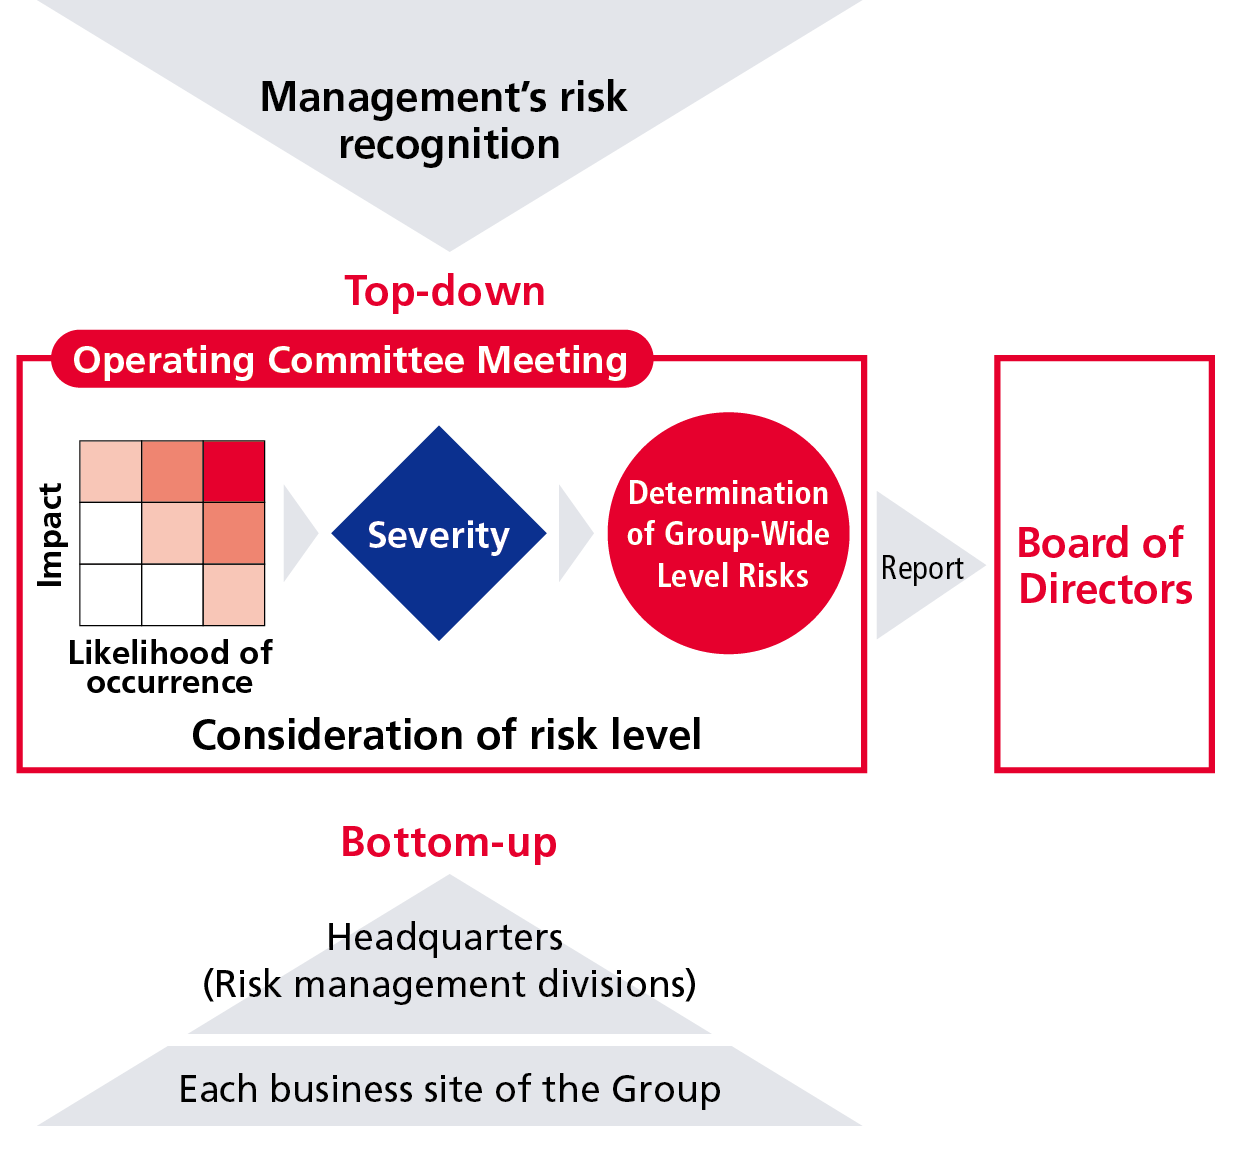
We have positioned the Operating Committee, which is an advisory body to the CEO, at the center of executive decision-making in ERM. The Operating Committee determines the material risks to be managed, and the details of its deliberations are also reported to the Board of Directors. We have also built a framework for regularly reporting to the Board of Directors the details of the risks subject to management as determined by the Operating Committee, the status of the response to such risks, and the status of the response to incidents.
Determination of Group-Wide Level Risks (Risk Assessment)
Enterprise Risk Management (ERM) System
ERM Operational Status
◆Risk Management
We conduct risk assessments once a year covering each of our sites around the world. At the start of the risk assessment, we disseminate the risk recognition of the CEO and of the heads of each risk management division (the heads of the business division headquarters and the heads of the functional division headquarters). The assessments are carried out by the risk response divisions and risk management divisions in accordance with these risk recognitions. Risks are weighted according to likelihood of occurrence and impact of residual risk. For particularly material risks, risks subject to management are determined after deliberation by the Operating Committee. The Operating Committee meets to discuss not only risks identified through the bottom-up approach but also risks that are important for management strategy (including emerging risks), which are identified by corporate leadership.
Risks subject to management are categorized into Group-wide level risk determined by the Operating Committee and risks to be managed by each headquarters and site (“headquarters-level risk” and “on-site level risk” respectively). Following this process, we carry out response activities and monitoring for these risks. The response status for Group-wide level risks is regularly reported to the CEO and CFO, as well as to the Board of Directors. When a material risk arises during the fiscal year, it is added as a new risk to be managed.
◆Incident Management
Whenever an incident meets certain reporting criteria, an initial report is made to the risk management division responsible for that risk area the incident falls under. Particularly serious incidents are also reported to the CEO and CFO. Following such reports, an action plan is formulated for each incident. As the plan is executed, the status of the response is reported regularly until the incident is resolved.
◆ERM Training
We carry out regular ERM training to upgrade the level of ERM and foster a sound risk culture.
ERM Operational Status List
| Activities | Frequency | Notes |
|---|---|---|
| Risk assessment | Once a year | When new risks arise during the fiscal year, they are registered as risks subject to management. |
| Regular reporting of Group-wide level risks and serious incidents to the CEO and CFO | Once a month | Group-wide level risks, the occurrence of incidents, and the status of responses are reported to the CEO and CFO by the risk management divisions or the Risk Management Oversight Division. Particularly material issues are also reported at meetings of various committees chaired by the CEO. |
| Reporting to the Board of Directors | Several times a year | The status of ERM is reported by the CEO or the head of the Risk Management Oversight Division. |
| ERM educational activities | As necessary | In April 2026, we held a training session for officers including the CEO and CFO. We also hold e-learning programs for employees every year (approximately 400 employees at 28 Group companies participate). |
In addition to ERM as described above, we manage individual risks in each business process. For example, we operate our original NSK Product Development System (NPDS) as a mechanism for managing quality risk in each process from product planning though development and mass production. In addition, when introducing equipment, we carry out a risk assessment related to safety aspects and work to reduce risks.
Material Risks in FY2026
| Risk Item | Details of Representative Risks | Countermeasures |
|---|---|---|
| (1) Geopolitical risks |
|
|
| (2) Risks associated with technological innovation |
|
|
| (3) Risks associated with safety, prevention of fire, and natural disasters |
|
|
| (4) Risks associated with quality |
|
|
| (5) Risks associated with the environment |
|
|
| (6) Risks associated with compliance |
|
|
| (7) Risks associated with human resources and labor |
|
|
| (8) Risks associated with procurement |
|
|
| (9) Risks associated with DX and information security |
|
|
| (10) Risks associated with mid- to long-term improvement in corporate value |
|
|